- RATs, or Remote Access Trojans (aka Remote Administration Tools), can give hackers total remote control of any compromised system(s). Once this type of malware payload is successfully delivered, through a phishing email, USB delivery or a malicious site, a hacker can easily get up to all kinds of costly mischief.
- This week, reports surfaced that a banking Trojan employing RAT technology known as Neverquest is poised to explode in the coming months.
- What do RATs do?
- “Put simply, a RAT is malware that gives criminals a backdoor to the infected system.
- Once a RAT payload has been delivered, a hacker will have all the access and privileges to everything on the system or device the user does.
- Most APTs (Advanced Persistent Threats) employ some kind of RAT technology because of the absolute power it gives an attacker to do basically whatever they want.
Monday, December 9, 2013
Regular Testing Essential to Stop Hacker Access

Sunday, December 8, 2013
Huawei security centre in UK gets security clearance
- Huawei supplies software and equipment which channels phone calls and data around Britain and has found itself at the centre of a debate, particularly in the United States, over whether it is a risk for governments to allow foreign suppliers access to their networks
- Britain will clear Chinese telecoms equipment firm Huawei to run a UK-based cyber security centre if it agrees to tighter rules to allay spying and hacking fears, a person familiar with the matter said.
- Check detailed news at http://articles.timesofindia.indiatimes.com/2013-12-05/hardware/44806476_1_potential-chinese-state-influence-huawei-cyber-security.
2M Facebook, Gmail, Twitter Passwords Stolen in Massive Hack
- Hackers have stolen usernames and passwords for nearly two million accounts at Facebook, Google, Twitter, Yahoo and others, according to a report released this week.
- The massive data breach was a result of keylogging software maliciously installed on an untold number of computers around the world, researchers at cybersecurity firm Trustwave said.
- The virus was capturing login credentials for key websites over the past month and sending those usernames and passwords to a server controlled by the hackers
- On Nov. 24, Trustwave researchers tracked that server, located in the Netherlands. They discovered compromised credentials for 93,000 websites, including:
318,000 Facebook accounts
70,000 Gmail, Google+ and YouTube accounts 60,000 Yahoo accounts 22,000 Twitter accounts 9,000 Odnoklassniki accounts (a Russian social network) 8,000 ADP.accounts 8,000 LinkedIn accounts - http://www.8newsnow.com/story/24135669/2-million-facebook-gmail-twitter-passwords-stolen-in-massive-hack
Saturday, December 7, 2013
Microsoft Beefs Up Encryption After NSA Spying Reports
- In response to reports that the feds are spying on tech firms' data as it moves between servers, Microsoft today pledged to step up encryption across its services.
- If true, NSA spying could "seriously undermine confidence in the security and privacy of online communications," Microsoft's general counsel, Brad Smith, said in a blog post.
- Smith said Office 365 and Outlook.com customer content is already encrypted when traveling between customers and Microsoft, while most Office 365 workloads as well as Windows Azure storage are now encrypted in transit between data centers.
- The NSA denied those allegations. "NSA is a foreign intelligence agency. And we're focused on discovering and developing intelligence about valid foreign intelligence targets only."
- Read more at ..http://www.pcmag.com/article2/0,2817,2427962,00.asp?mailingID=4A8C526FE94DD7A9EACC9565528CC0A8
Sunday, December 1, 2013
The Estonian Cyberwar and Its Implications for U.S. National Security
On April 26, 2007, the small Baltic state of Estonia experienced the first wave of denial-of-service (DoS) attacks. Accompanied by riots in the streets, these cyberattacks were launched as a protest against the Estonian government’s removal of the Bronze Soldier monument in Tallinn, a Soviet war monument erected in 1947. These attacks targeted prominent government websites along with the websites of banks, universities, and Estonian newspapers. After three weeks, the attacks ceased as suddenly as they had begun, but not before the Estonian government undertook measures to block all international web traffic, effectively shutting off the “most wired country in Europe” from the rest of the world.
Forensic analysis by US for future defense
http://www.iar-gwu.org/node/65
Forensic analysis by US for future defense
http://www.iar-gwu.org/node/65
Estonia’s experience in handling the cyber attacks of 2007 has positioned the country as a thought leader in cyber security.
A cyber attack against a country seems like something out of a science fiction movie. However, a perfect storm of political controversy and successful psychological warfare turned this into a reality in Estonia, when in 2007 the relocation of a Soviet World War II memorial started an unprecedented unrest in the country’s capital that has later been labelled the Bronze Night .
Read full report at Turning-around-2007-cyber-attack-lessons-estonia
Read full report at Turning-around-2007-cyber-attack-lessons-estonia
Which is the commercial value of a hacked email account in the underground?
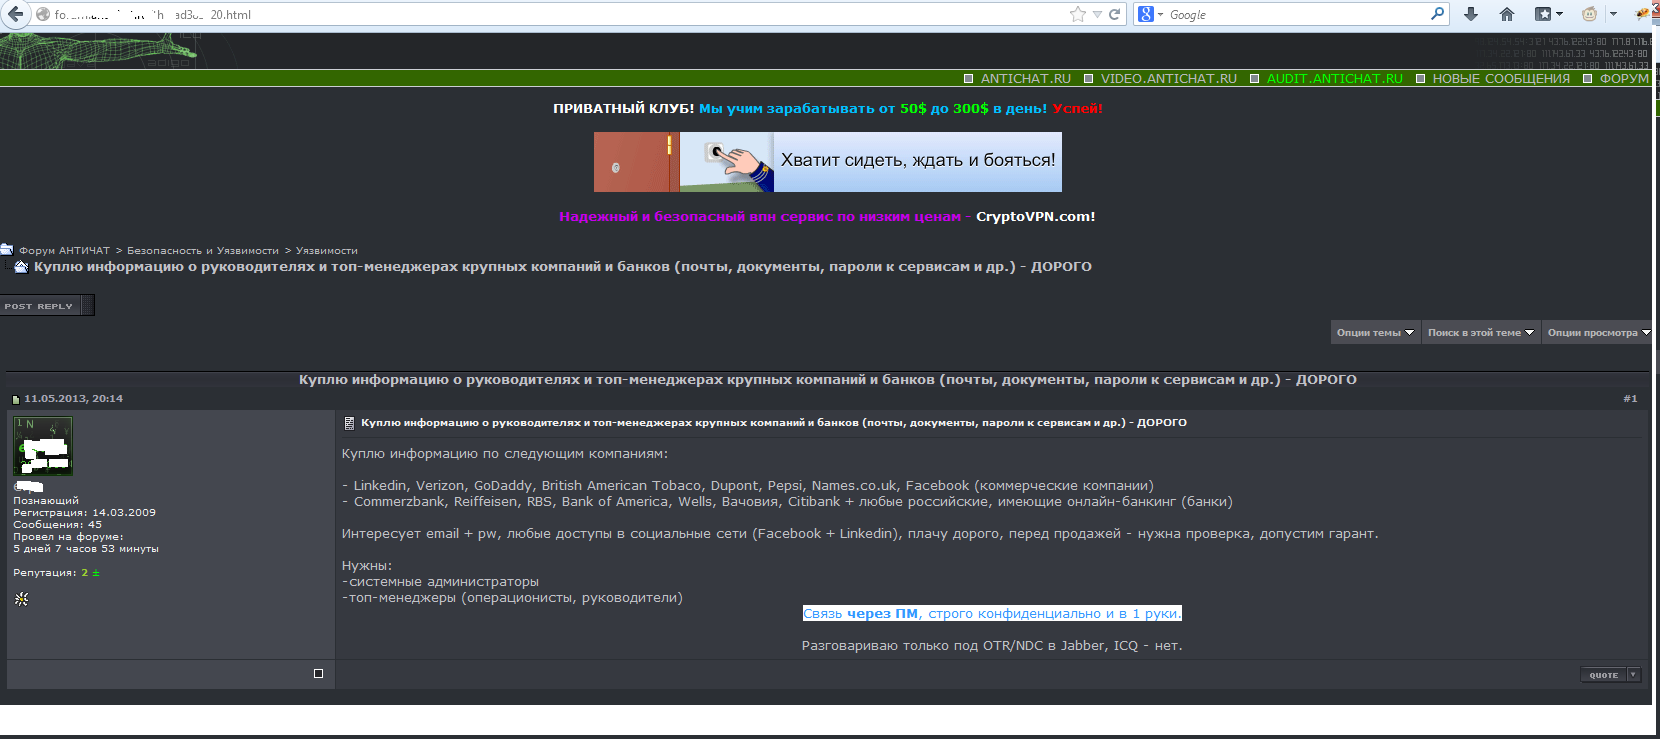
In the above image is reported a post from an underground forum that demonstrates the hacker’s interest to confidential data on CEO and top management of different well known brands, following the translation from Russian:
“Will buy information about the following companies:
- Linkedin, Verizon, GoDaddy, British American Tobaco, Dupont, Pepsi, Names.co.uk, Facebook (private companies)
- Commerzbank, Reiffeisen, RBS, Bank of America, Wells, Wachovia, Citibank + any russians, having online-banking
Interested in email + password, any stolen accounts of its employees in social networks (Facebook + Linkedin), will pay good, before selling need to have a garant and checking.
Interested in hacked accounts and data on:
- sustem administrators;
- top managers (operational managers, heads of the departments)
Reach me only through PM, confidential and in 1 hands
WIll talk only under OTR/NDC encryption in Jabber, don’t use ICQ “
Read More at http://goo.gl/LIcQR5
Friday, November 29, 2013
Mobile OS Wars: Samsung Introduces Tizen
Android, ChromeOS, Windows for phone, iOS, Google, Microsoft and now Samsung.
They are all having their own Os but now another competitor in the Market Samsung with Tizen.
As Mozilla prepare to launch a new Firefox-based operating system (OS) for cheaper phones in emerging markets, Samsung is taking on iOS, Android and Windows Phone with Tizen.
Source: http://www.techopedia.com/2/28205/trends/the-laws-of-computing
They are all having their own Os but now another competitor in the Market Samsung with Tizen.
As Mozilla prepare to launch a new Firefox-based operating system (OS) for cheaper phones in emerging markets, Samsung is taking on iOS, Android and Windows Phone with Tizen.
What is Tizen?
Tizen is a fully featured operating system developed by Samsung, and it’s designed to run on Samsung Galaxy S4 phones, as well as TVs and other connected devices from the Korean company.Why is Tizen Happening? Doesn’t Samsung use Android?
Yes, most Samsung smartphones and tablets use Android, and this means that Google can sell apps, music and movies on each product. It seems Samsung want a piece of that pie. Tizen is an OS set up by Samsung but, crucially, Intel also is open for use on smart TVs and even car entertainment and navigation. Soon after Google announced they were buying Motorola and making a new smartphone, Samsung issued a statement saying, "We plan to release new, competitive Tizen devices within this year and will keep expanding the lineup depending on market conditions."How is Tizen Different From Android?
Like Firefox OS, Tizen uses the HTML5 Web format, which means that mobile and desktop apps are easily accessible on the OS without the need for extra apps or plug-ins. This also makes it easier to develop Tizen than, say, iOS, because Tizen is an open format. This means developers can experiment with minimum outlay or third party authorization. The backbone of the system is Linux, a popular development tool. Wannabe developers also have been offered $4 million in prize funds from the Tizen Foundation for making impressive apps and games. Samsung is keenly aware that Microsoft and BlackBerry smartphones are still suffering from a lack of key apps, compared to iOS and Android.Will Tizen use Android Apps?
Yes, but not as standard. A setting allows native use of Android apps, but expect the push to be on evolved versions that are unique to Tizen in a similar way to the Samsung Edition of popular Android apps, like Trip Advisor.When Will Tizen be Released?
On November 9, 2013, Tizen released its latest version 2.2.1 platform and software development kit (SDK). Samsung's principal engineer, Alvin Kim, spoke about the relationship between Android and Tizen, commenting that he hopes “some devices will be given to the market by the end of [2014].” Leaks have hinted at a Galaxy S4 running the OS, fueling speculation that it may reach existing smartphones, including the Galaxy S3, by early 2014.Didn’t Samsung do This Before?
Yes, Bada was an early phone OS, and Intel also had a mobile operating system. Both failed in the face of iOS and Android. However, Tizen is an evolved joint effort between the two companies. Samsung is a major player in the smartphone, TV and tablet market, so there’s more chance of a bigger uptake, particularly in the East and for first-time smartphone users not already comfortable with iOS and Android. As a footnote, Samsung sold over 400 million smartphones in 2012 alone, globally.What Does Tizen Look Like?
The color scheme and tiles blend the new look of iOS 7 with Windows Phone. Designed for Samsung fans and new smartphone owners, the focus is on speed and simplicity, although it’s expected to be highly customizable. J.K. Shin, Samsung's co-CEO, told CNET that Tizen is more than just "a simple alternative for Android." Tizen also will allow users to open multiple windows to simultaneously view email and a Web browser, blurring the lines between desktop and mobile. Modern BlackBerry users will be familiar with the ability to preview a second screen while using another.Will a Tizen Smartphone be Powerful?
A Qualcomm processor is expected to power a dedicated Tizen smartphone, but a 720p display on a prototype suggests that the smartphone will be a powerful but affordable device. After all, the key aim is to dent the spread of iOS devices, and a Tizen smartphone is expected to be a key rival for the iPhone 5c. Last year's Tizen smartphone prototype featured a 1.2 Ghz processor and 1 GB of random access memory (RAM), offering a similar spec to a Nexus smartphone. Interestingly, both Fujitsu and NEC are developing Tizen smartphones that are likely to be high-end devices aimed toward Japanese business users.Source: http://www.techopedia.com/2/28205/trends/the-laws-of-computing
Domain Name Server Amplification Attack
New type of DDoS wherein server is sent a large amount of data with the, the intent is to make a system unavailable to legitimate users.
Wanted: Cyber guards for India
More job opportunities for cyber security professionals;
Even as India proclaims itself to be the hub of information technology, it has not been able to take on cyber attacks from hackers across the world. This is due to lack of cyber security professionals.
“India is a country where youngsters are encouraged to take up jobs of application programming and not system programming, which is essential to equip one’s own desktop, one’s organization and his or her country, against cyber attacks,” noted an expert in cyber security on the event of World Computer Security Day which falls on Friday.
Government itself has admitted that there are less that 1,000 people in the country who are experts in system side programming while the demand is for around 5 lakh professionals, noted Dr B Muthukumaran, cyber crime consultant for the Tamil Nadu police.
“Policing the cyber world may not be a job which a regular policeman can execute and calls for special cyber investigative skills and exposure to associated cyber laws. There should be more technically sound professionals in the force who can understand and handle cases,” noted another expert who has assisted intelligence agencies in cyber crime cases.
Indian youth focus more on application software and refuse to be trained in system side development because the easily available job segment is in application development jobs in the information technology world. However in countries like China, Germany and US, youngsters are being trained to focus on system side programming, thus helping those countries to develop their defences in the cyber world, noted Dr Muthukumaran, who is also DGM, Institute of Technology Management & Research, Chennai.
The recently announced information security policy has opened up many entrepreneurial opportunities for youngsters trained in system side programming. The future world calls for specialization and it is difficult to survive without cyber security guards.
Reference http://goo.gl/RhiuoO
How to change the key in Windows 8
When I upgraded from windows 7 ultimate to windows 8, it was all smooth and the there was no problem. When I clicked on update now, the message was displayed that "Activate windows before updating"
However all trouble started when I wanted to activate the Windows 8 by entering the KEY.
Clicking on activate link said Windows cannot be activate now, contact your administrator!
For complete 72 hour I kept on repeating the process of installing and uninstalling thinking that there would have been some problem in installation.
Then I came across this process as given below
To change the product key without first activating Windows, use one of the following methods:

4. This is the method I followed to activation.
However all trouble started when I wanted to activate the Windows 8 by entering the KEY.
Clicking on activate link said Windows cannot be activate now, contact your administrator!
For complete 72 hour I kept on repeating the process of installing and uninstalling thinking that there would have been some problem in installation.
Then I came across this process as given below
To change the product key without first activating Windows, use one of the following methods:
Method 1
- Press Windows+r key.
- Type Command in run
3. Then press enter. you will be taken to Screen where you enter the Activation key.
 |
| Type slui 3 at command prompt |

4. This is the method I followed to activation.
Method 2
- Swipe in from the right edge of the screen, and then tap Search. Or, if you are using a mouse, point to the lower-right corner of the screen, and then click Search.
- In the search box, type Slui.exe 0x3.
- Tap or click the Slui.exe 0x3 icon.
- Type your product key in the Windows Activation window, and then click Activate.
Method 3
Run the following command at an elevated command prompt:Cscript.exe %windir%\system32\slmgr.vbs /ipk <Your product key>
You can also use the Volume Activation Management Tool (VAMT) 3.0 to change the product key remotely, or if you want to change the product key on multiple computers.Thursday, November 28, 2013
Ransomware virus threat getting worse
Taking advantage of anonymous payment services, cyber criminals are increasingly using a malicious software 'ransomware' that holds a computer hostage until the victim pays to free it, online security firm McAfee says.
"Ransomware has become an increasing problem during the last several quarters and the situation continues to worsen. The number of new, unique samples this quarter is greater than 312,000, slightly less than last quarter but still the second highest figure recorded by the firm," the McAfee Labs Threats Report Third Quarter 2013, said.
"Ransomware has become an increasing problem during the last several quarters and the situation continues to worsen. The number of new, unique samples this quarter is greater than 312,000, slightly less than last quarter but still the second highest figure recorded by the firm," the McAfee Labs Threats Report Third Quarter 2013, said.
Petroleum Ministry warns PSU oil companies of cyber attacks
Following an advisory by the Indian Computer Emergency Response Team (CERT), the Petroleum and Natural Gas Ministry has alerted all the heads of oil marketing companies (OMCs) about the possibility of cyber attacks.
http://goo.gl/z9miIx
Indian tweens use risky or low level security passwords
Indian tweens, children between the age of 8-12 years, are enthusiastically adopting Internet using multiple devices, but use risky or low level security passwords, a survey by cyber security major McAffee revealed.
McAfee's Tweens and Technology Report 2013 said online tweens are potentially vulnerable to risky behaviour on the Internet a good number of them have chatted to someone online that they didn't know previously.
A disturbing trend on the rise among tweens is their apathy towards their own online safety. 58 per cent of the respondents surveyed use risky or low level security passwords online and Almost half of the tweens surveyed share information about themselves over FB (41 per cent), it added.
Another dangerous trend that the survey by the US-based firm revealed is that Indian tweens are becoming more trusting of the virtual world to familiarise themselves with unknown people, in spite of being aware that it is risky.
http://zeenews.india.com/news/net-news/tweens-fast-adopting-internet-but-apathetic-towards-security_892783.html
Sunday, November 24, 2013
Top Ten Biggest Cyber Crimes
Though slightly outdated but still gives useful information on cyber attacks in modern times
Source : http://www.infosecisland.com/blogview/17807-Top-Ten-Biggest-Cyber-Attacks-Of-All-Time.html
Source : http://www.infosecisland.com/blogview/17807-Top-Ten-Biggest-Cyber-Attacks-Of-All-Time.html
News Super Computing 13: GPUs would make terrific network monitors
- A network researcher at the U.S. Department of Energy's Fermi National Accelerator Laboratory has found a potential new use for graphics processing units -- capturing data about network traffic in real time.
- GPU-based network monitors could be uniquely qualified to keep pace with all the traffic flowing through networks running at 10Gbps (gigabits per second) or more, said Fermilab's Wenji Wu.
- What he is trying to tell that all the present technologies and tools used have their limitation and their traffic monitoring capabilities are extremely fault prone
- CPUs don't have the memory bandwidth or the compute power to keep pace with the largest networks in real time. As a result, they can drop packets.
- Thus GPU are the future.
- Checkout more at http://goo.gl/Qqmy6N
Thursday, November 21, 2013
Aviation industry vulnerable to cyber attacks: IATA
- Think about the scenario when you suddenly find that the destination of your flight has been changed because the navigation system has been hacked and it has been set to some other country. And most scary is the fact that all this is because of a prank by 12 year old.
- Faced with cyber security threats, the aviation industry, which has spent over US$ 100 billion on security since 9/11, should share best practices and partner with governments to adapt to new challenges and tackle them, airlines' body IATAhas said.
- Noting that aviation now relies on computer systems for almost every aspect of the business, leaving it potentially vulnerable to cyber attack, IATA asked the industry, governments, regulators and manufacturers to work together to share best practices and mitigation strategies.
- Checkout the complete article at http://goo.gl/VvuKH5
Spurt in attacks on Indian websites
Cyber attacks against Indian websites have increased exponentially in 2013, despite the government supposedly building a credible cyber defence system.
According to confidential reports by CERT-In (Indian Computer Emergency Response Team), 4,191 Indian websites were defaced or hacked into in August, 2,380 in July, 2,858 in June and 1,808 in May. An overwhelming percentage of these attacks occurred in the .in domain, whose servers are in India - 80% in June and over 60% thereafter.
Checkout full article here http://goo.gl/N9aTWB
Checkout full article here http://goo.gl/N9aTWB
Snowden Likely Used SSH Keys to Access Classified NSA Data
Using public statements from Edward Snowden and NSA officials, digital-certificate firm Venafi pieces together a likely scenario for how the former contractor accessed classified documents.
Edward Snowden has not publicly stated how he leveraged his privileged access to certain servers and top-secret information at the National Security Agency into a wider fishing expedition, netting classified secrets that he had no clearance to access. The NSA hasn't provided much insight either.This week, however, security researchers at certificate-management firm Venafi threw their collective hat into the ring, posting an analysis stating that Snowden likely used authentication keys to give his account privileged access to other servers in the network. Secure shell (SSH) keys are frequently used by system administrators to log into remote computers without a password, and Snowden likely gained access to others' keys or to privileged accounts and inserted his own keys, the company said.
The most significant clue is General Keith Alexander's testimony in which the NSA chief reportedly stated that Snowden "fabricated digital keys" to gain access to classified systems, Jeff Hudson, CEO of Venafi, told eWEEK.
"It all comes back to one thing: 'He fabricated the SSH keys,'" he said. "What he did was he allowed himself access to other systems and in the process he elevated his privilege."
More news at http://www.eweek.com/security/snowden-likely-used-ssh-keys-to-access-classified-nsa-data-venafi.html
Subscribe to:
Posts (Atom)
Proud Blogger

